
The 'cupcake' hack
Discussion


ha ha - this excellence!
http://www.telegraph.co.uk/news/uknews/terrorism-i...
but something i've always wondered - cue IT boys and girls - how the hell do you 'hack' a system? whats the point of entry?
http://www.telegraph.co.uk/news/uknews/terrorism-i...
but something i've always wondered - cue IT boys and girls - how the hell do you 'hack' a system? whats the point of entry?
Loads and loads of different ways. From the brute force one used on ACS:Law (DDoS it 'til it reboots, amusingly allowing the world + dog access to the root) to really complicated code injection assaults (using special codes that cause content databases and the like to do odd things).
Quite a high chance it was just a case of figuring out what software the server was running, navigating to the maintenance page, then logging in using username "admin" and password "password" though.
Quite a high chance it was just a case of figuring out what software the server was running, navigating to the maintenance page, then logging in using username "admin" and password "password" though.
Unless times have changed, most illicit system access is gained by weedling out username and password details from an authorised user by:- dumpster diving, or plausible conman questionning "drong dring... dring dring... Hello, this is IT support here, we've had a report of an issue with x.... can you let us have the username and password you were logged in with when it occurred.... " and so on. Boringly low tech really.
davislove said:
but something i've always wondered - cue IT boys and girls - how the hell do you 'hack' a system? whats the point of entry?
Have a read of the forums over at www.astalavista.comEinion Yrth said:
Unless times have changed, most illicit system access is gained by weedling out username and password details from an authorised user by:- dumpster diving, or plausible conman questionning "drong dring... dring dring... Hello, this is IT support here, we've had a report of an issue with x.... can you let us have the username and password you were logged in with when it occurred.... " and so on. Boringly low tech really.
 The users are usually the weakest point in any "secure" system.
Why cupcakes?
Why not tweak the original instructions slightly so they pop themselves during the making of the bomb? Now *that* would have been both highly amusing and rid us of a few wannabe terrorists (would probably have taken a while to spot).
As it is they'll just move their site elsewhere over a nice cup of tea and a cake.

davislove said:
ha ha - this excellence!
http://www.telegraph.co.uk/news/uknews/terrorism-i...
but something i've always wondered - cue IT boys and girls - how the hell do you 'hack' a system? whats the point of entry?
This is apparently quite common:http://www.telegraph.co.uk/news/uknews/terrorism-i...
but something i've always wondered - cue IT boys and girls - how the hell do you 'hack' a system? whats the point of entry?
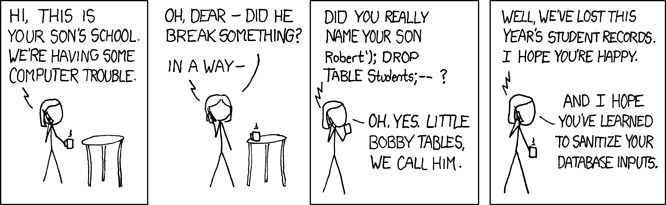
Shouldn't be, but it's how Sony recently got f
 ked. Well, it's one of the ways in which Sony recently got fked. (Aside; Sony's recent security travails have cost the company $170 million. And it's rising, because it seems like it's every week I read about a different bit of Sony that gets bummed sans lube)
Even so-called Internet Security Experts get f
ked. This is a very interesting article about how HBGary got turned over by Anonymous.Edited by CommanderJameson on Thursday 9th June 00:38
Caulkhead said:
Have a read of the forums over at www.astalavista.com
My word, this brings back memories 
Murph7355 said:
Why cupcakes?
Why not tweak the original instructions slightly so they pop themselves during the making of the bomb? Now *that* would have been both highly amusing and rid us of a few wannabe terrorists (would probably have taken a while to spot).
As it is they'll just move their site elsewhere over a nice cup of tea and a cake.
Interesting point, why dont they flood whatever regions of the internet with fake websites from these fanatics with the type of info you described above?! Surely a few would bite and end up topping themselves in the process. It cant be so hard for someone with the right skills to make a site look like its from Terry-Wrist or whoever is running Al-QalWhy not tweak the original instructions slightly so they pop themselves during the making of the bomb? Now *that* would have been both highly amusing and rid us of a few wannabe terrorists (would probably have taken a while to spot).
As it is they'll just move their site elsewhere over a nice cup of tea and a cake.
Mark.H said:
Murph7355 said:
Why cupcakes?
Why not tweak the original instructions slightly so they pop themselves during the making of the bomb? Now *that* would have been both highly amusing and rid us of a few wannabe terrorists (would probably have taken a while to spot).
As it is they'll just move their site elsewhere over a nice cup of tea and a cake.
Interesting point, why dont they flood whatever regions of the internet with fake websites from these fanatics with the type of info you described above?! Surely a few would bite and end up topping themselves in the process. It cant be so hard for someone with the right skills to make a site look like its from Terry-Wrist or whoever is running Al-QalWhy not tweak the original instructions slightly so they pop themselves during the making of the bomb? Now *that* would have been both highly amusing and rid us of a few wannabe terrorists (would probably have taken a while to spot).
As it is they'll just move their site elsewhere over a nice cup of tea and a cake.
Watching terry websites provides short and long term gains.
Einion Yrth said:
Unless times have changed, most illicit system access is gained by weedling out username and password details from an authorised user by:- dumpster diving, or plausible conman questionning "drong dring... dring dring... Hello, this is IT support here, we've had a report of an issue with x.... can you let us have the username and password you were logged in with when it occurred.... " and so on. Boringly low tech really.
Or hang around near the office with a big box of Mars bars targeting the larger ladies:http://www.theregister.co.uk/2008/04/16/password_s...
There are many system administrators that use seriously weak root passwords because they think they are 'clever'.....
I still know of a system where the password is 'letmein'.
Staff turnover is the biggest problem.
Systems where the root password is a one time use log on are better. A seperate stand alone system generates a new password every time. The beauty of this is the term 'stand alone'. As is under lock and key and no network connections......
Corsair7 said:
There are many system administrators that use seriously weak root passwords because they think they are 'clever'.....
I still know of a system where the password is 'letmein'.
Staff turnover is the biggest problem.
Systems where the root password is a one time use log on are better. A seperate stand alone system generates a new password every time. The beauty of this is the term 'stand alone'. As is under lock and key and no network connections......
I wanted to get at the data in a secured CD based SQL database once.I still know of a system where the password is 'letmein'.
Staff turnover is the biggest problem.
Systems where the root password is a one time use log on are better. A seperate stand alone system generates a new password every time. The beauty of this is the term 'stand alone'. As is under lock and key and no network connections......
I got a free trial of an MSOffice password hacker, ran it and it said the password was...
kli****
Hmmm....let me think...IT geek...
klingon perhaps?
Oh, yes!
Gassing Station | News, Politics & Economics | Top of Page | What's New | My Stuff